CISO LEADERSHIP & PENETRATION TESTING

Security leadership that moves
your business forward.

When an enterprise customer asks for security evidence, an audit is approaching, or your organization needs dedicated security leadership, Cybecs maps the gaps, builds the annual workplan, and works alongside your teams to execute.

Outsourced CISO leadership, regulatory compliance, and offensive security delivered by one team.

STRUCTURED DELIVERY

How the first 30 days
of an engagement run.

  1. 01

    Environment & regulatory mapping

    Review cloud infrastructure, core systems, vendors, and applicable frameworks (ISO 27001, SOC 2, GDPR, Amendment 13).

  2. 02

    Risk assessment & gap rating

    Identify technical and governance gaps and prioritize remediation in a 4×4 risk matrix by likelihood and business impact.

  3. 03

    Annual workplan & ongoing delivery

    Build an annual Gantt workplan with engineering owners, tailored policies, and executive tracking in the client portal.

START WITH WHAT MATTERS TO YOU

What brings you here?

Choose the challenge on your mind. See how we approach it and what the work can include.

WHAT THE WORK CAN INCLUDE

Leadership with a working plan

An outsourced chief information security officer (CISO) connects management priorities with the work your teams do. We assess the current position and build a program around your organization.

  • Risk and needs assessment
  • An action plan with clear ownership
  • Progress reviews and management reporting
We agree on the scope and deliverables after understanding your organization.

WHAT THE WORK CAN INCLUDE

From requirements to practical work

We review the relevant requirements and what you already have. We identify gaps, agree on actions and help organize the evidence you need.

  • A gap assessment
  • A control implementation plan
  • Documentation and audit preparation
We agree on the scope and deliverables after understanding your organization.

WHAT THE WORK CAN INCLUDE

Put your systems to the test

We agree on the scope and conditions before testing. Penetration testing helps identify weaknesses and prioritize remediation based on risk.

  • An agreed testing scope
  • Findings with remediation guidance
  • Retesting within the agreed scope
We agree on the scope and deliverables after understanding your organization.

WHAT THE WORK CAN INCLUDE

Security built into technical work

We review architecture, access and development processes. We work with your cloud and engineering teams on changes that fit their systems and workflows.

  • Architecture and access reviews
  • Prioritized hardening recommendations
  • Security in the development lifecycle
We agree on the scope and deliverables after understanding your organization.

Dealing with a security incident? Explore incident response

TRUSTED BY SECURITY & ENGINEERING TEAMS AT
Founded 2020
Israel
ISO/IEC 27001:2022 Certified

CYBECS / THE TEAM

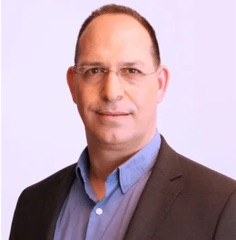
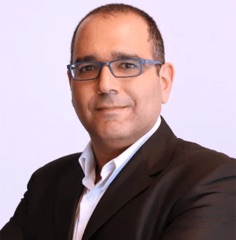
People behind the recommendations.

Meet the co-founders of Cybecs and explore their professional backgrounds. Risk leadership and technical work come together in one team.

CYBECS / HOW WE WORK

How ongoing engagements run inside our management platform.

Every engagement is managed in the Cybecs workspace, bringing your risk register, annual workplan, policies, and remediation tracking into one structured environment for leadership and engineering.

STEP 1 · ORGANIZATION & REGULATORY SCOPE

Cybecs Portal

Aligning controls and requirements to your actual environment

Core infrastructure & systems
AWS, Microsoft 365, GitHub, production SaaS & internal systems
Asset scope
Applicable standards & regulations
ISO/IEC 27001:2022, SOC 2, GDPR, Israeli Privacy Law Amendment 13
Framework map
Control applicability
Scopes assessments and policies to the systems and data you actually run
Scoped controls
Portal access is included as part of Cybecs engagements. Schedule an introductory call

AI adoption without uncontrolled risk.

Identity, authorization, data classification, model boundaries, agent permissions, logging, human approval: governed the way real enterprise risk gets governed, with controls tailored to the systems your organization uses.

AI Security Strategy Session

See the full AI Security offering, then book a 30-minute working session mapping your actual AI risk surface to concrete controls, focused on your systems and the controls they need.

Regulatory and operational context we already understand.

Financial Services
Insurance
Technology / SaaS
Retail & E-commerce
Manufacturing
Aviation & Transportation
Government / Public Sector
Energy

Our work with The Pool.

INSURANCE
The Pool (HaPool)
Challenge
Ongoing cybersecurity leadership, regulatory compliance, and technical assurance for Israel's compulsory motor insurance pool.
Scope
Information Security Manager (CISO), regulatory and technological assessments, and penetration testing.
Read the full story →

Executive depth. Hands-on execution.

»

Executive cybersecurity leadership with hands-on technical depth.

»

Offensive and defensive capabilities under one team.

»

Regulatory knowledge translated into technical controls and evidence.

»

Support across boardroom, IT, security, engineering and compliance teams.

»

Practical delivery for regulated and enterprise environments.

Amendment 13 Readiness Check

A short, structured self-assessment against Israel's updated Protection of Privacy Law. See where your organization stands before a regulator asks.

Start the Readiness Check

LET’S GET TO KNOW YOU

The next step is a conversation.

Tell us what is on your mind, what you have in place and what needs to happen next. Together, we can explore where we can help and what to look at first.

Let’s talk about your organizationYou do not need a requirements document to get in touch.